English
การแนะนำ
คลินิกทันตกรรมแห่งหนึ่งต้องการลดการไม่มาปรากฏตัว แผนกต้อนรับจึงเริ่มส่งข้อความหาคนไข้โดยใช้โทรศัพท์ส่วนตัว "สวัสดีแซม พรุ่งนี้การติดตามผลคลองรากฟันของคุณคือพรุ่งนี้เวลา 9 โมงเช้า" วิธีนี้ใช้งานได้จนกว่าจะมีการแชร์โทรศัพท์ของผู้ป่วยกับสมาชิกในครอบครัวที่ไม่ทราบเกี่ยวกับขั้นตอนดังกล่าว
สามารถส่งข้อความตามมาตรฐาน HIPAA ได้ แต่มันมีกฎเกณฑ์และคลินิกข้างต้นได้ขยายออกไปแล้ว
คู่มือนี้จะอธิบายการส่งข้อความที่สอดคล้องกับ HIPAA เป็นภาษาอังกฤษธรรมดา โดยครอบคลุมถึงสิ่งที่กฎกล่าวไว้ ข้อความใดปลอดภัยกว่า สิ่งที่ควรถามผู้จำหน่ายการส่งข้อความ และวิธีการตั้งค่ากระบวนการง่ายๆ เป็นข้อมูลทั่วไป ไม่ใช่คำแนะนำทางกฎหมาย เราตรวจสอบข้อความกฎใน 45 CFR ส่วนที่ 164 ในเดือนพฤศจิกายน 2026
ประเด็นสำคัญ
- HIPAA ไม่ได้ห้ามผู้ป่วยที่ส่งข้อความ ต้องมีการป้องกันที่เหมาะสมสำหรับข้อมูลด้านสุขภาพที่ได้รับการคุ้มครอง
- การส่งข้อความที่เป็นไปตามข้อกำหนดของ HIPAA ขึ้นอยู่กับวิธีการส่งข้อความของคุณ สิ่งที่คุณรวมไว้ และใครที่จัดการข้อความ ไม่ใช่ขึ้นอยู่กับคำว่า "SMS" เพียงอย่างเดียว
- แบ่งปันขั้นต่ำ การเตือนความจำแทบไม่จำเป็นต้องมีการวินิจฉัยหรือชื่อการรักษา
- หากผู้จำหน่ายจัดการข้อมูลผู้ป่วยให้กับคุณ คุณจะต้องมีข้อตกลงร่วมธุรกิจกับผู้ขาย
- การส่งข้อความด้านการดูแลสุขภาพจะทำงานได้ดีที่สุดเมื่อข้อความสั้น กำหนดเวลา และไม่มีรายละเอียดทางคลินิก
- ข้อความทางการตลาดและการแจ้งเตือนยังอยู่ภายใต้กฎหมายอื่นๆ เช่น TCPA
- ไม่มีเครื่องมือใดที่ทำให้คุณปฏิบัติตามได้ด้วยตัวเอง กระบวนการของคุณมีความสำคัญพอๆ กับซอฟต์แวร์ของคุณ
การส่งข้อความเป็นไปตามมาตรฐาน HIPAA หรือไม่
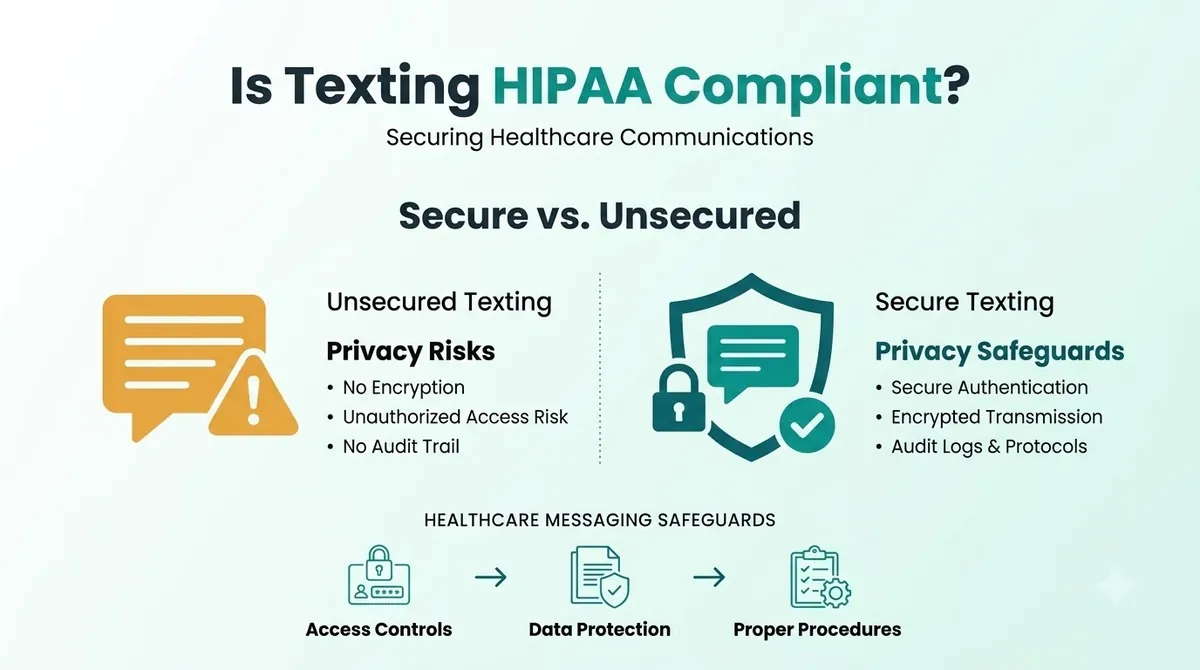
การส่งข้อความสามารถทำได้ในลักษณะที่เหมาะกับ HIPAA แต่การส่งข้อความธรรมดาไม่เป็นไปตามข้อกำหนดโดยอัตโนมัติ HIPAA คือชุดกฎสำหรับหน่วยงานที่ครอบคลุม เช่น แพทย์ คลินิก ทันตแพทย์ และแผนประกันสุขภาพ และสำหรับผู้ร่วมธุรกิจที่ทำงานให้กับพวกเขา ไม่ใช่ตราประทับที่คุณสามารถใส่ลงในประเภทข้อความได้
SMS มาตรฐานไม่ได้สร้างเป็นช่องทางที่เข้ารหัส ดังนั้น SMS ที่สอดคล้องกับ HIPAA จึงขึ้นอยู่กับวิธีการใช้งานของคุณ การเข้ารหัส SMS ไม่ใช่สิ่งที่การส่งข้อความธรรมดาให้คุณเป็นค่าเริ่มต้น ข้อความจะถูกส่งผ่านเครือข่ายผู้ให้บริการ อยู่บนโทรศัพท์ และสามารถแสดงบนหน้าจอล็อกได้ นั่นทำให้สิ่งที่คุณใส่ไว้ในข้อความ และผู้ที่สามารถดูโทรศัพท์ได้คือความเสี่ยงหลัก
ข้อมูลด้านสุขภาพที่ได้รับการคุ้มครอง (PHI) คือข้อมูลด้านสุขภาพที่สามารถเชื่อมโยงกับบุคคลได้ ชื่อและประเภทการนัดหมายเป็นตัวอย่างทั่วไป การส่งข้อความ PHI หมายความว่าคุณต้องการการป้องกันที่ตรงกับความเสี่ยง
กฎการส่งข้อความของ HIPAA โดยสรุป
| หัวข้อ | มันถามอะไรคุณ | มันมาจากไหน. |
|---|---|---|
| ความปลอดภัยในการส่งสัญญาณ | มาตรการทางเทคนิคเพื่อป้องกันการเข้าถึง PHI ที่ส่งผ่านเครือข่ายโดยไม่ได้รับอนุญาต | 45 CFR 164.312(จ) |
| การเข้ารหัส | เข้ารหัส PHI อิเล็กทรอนิกส์ทุกครั้งที่เห็นว่าเหมาะสม (รายการที่ระบุที่อยู่ได้) | 45 CFR 164.312(อี)(2)(ii) |
| จำเป็นขั้นต่ำ | จำกัด PHI ไว้เท่าที่จำเป็นสำหรับวัตถุประสงค์ | 45 CFR 164.502(ข) |
| ผู้ร่วมธุรกิจ | รับการรับประกันที่น่าพอใจจากผู้ขายที่จัดการ PHI | 45 CFR 164.502(e) และ 164.308(b) |
| การควบคุมการเข้าถึง | ตรวจสอบว่าใครกำลังเข้าถึง PHI และจำกัดการเข้าถึง | 45 CFR 164.312(ก) และ (ง) |
"ระบุที่อยู่ได้" ไม่ได้หมายความว่าเป็นทางเลือก หมายความว่าคุณประเมินความเสี่ยงและใช้มาตรการหรือเอกสารว่าทำไมสิ่งอื่นถึงดีพอๆ กัน
ผู้ป่วยที่ส่งข้อความ HIPAA: อะไรปกติดีและอะไรเสี่ยง
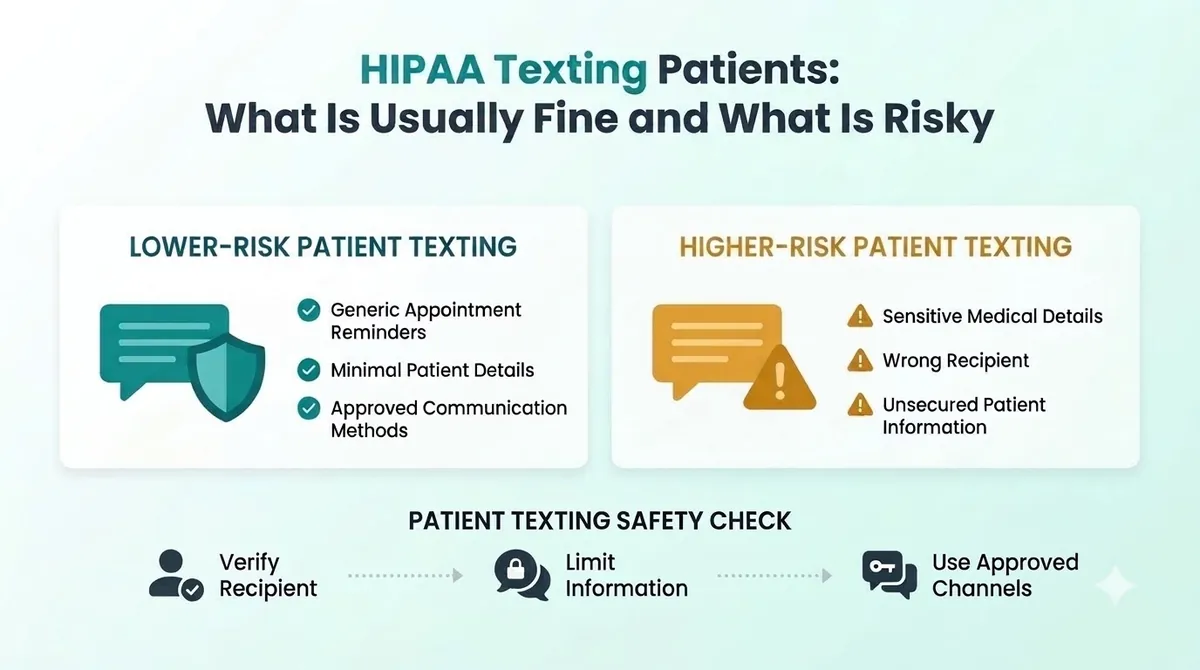
ข้อความที่ปลอดภัยที่สุดพูดน้อย พวกเขาชี้ผู้ป่วยไปยังสถานที่ที่ปลอดภัยเพื่อดูรายละเอียด
ตัวอย่างความเสี่ยงที่ต่ำกว่า (ข้อมูลน้อยที่สุด):
“สวัสดีแซม นี่เป็นการเตือนถึงการนัดหมายของคุณที่ Bright Smile Dental พรุ่งนี้ เวลา 9.00 น. ตอบ C เพื่อยืนยันหรือโทรหาเราตามหมายเลขบนบัตรของคุณ”
“เอกสารของคุณพร้อมแล้ว กรุณาเข้าสู่ระบบพอร์ทัลผู้ป่วยเพื่อดูพวกเขา”
ตัวอย่างความเสี่ยงที่สูงขึ้น (ข้อมูลมากเกินไป):
“สวัสดีแซม การติดตามผลคลองรากฟันของคุณคือพรุ่งนี้เวลา 9.00 น. ผลการตรวจของคุณพบว่ามีการติดเชื้อ”
“ใบสั่งยาสำหรับ [ชื่อยา] พร้อมสำหรับการวินิจฉัย [เงื่อนไข] แล้ว”
คู่แรกให้ขั้นต่ำ คู่ที่สองใส่รายละเอียดทางคลินิกไว้ในข้อความที่ใครก็ตามที่ถือโทรศัพท์สามารถมองเห็นได้ นี่คือเหตุผลที่เราแนะนำตัวอย่างข้อความ HIPAA ที่ไม่มีการวินิจฉัย ผลการทดสอบ หรือยา
การส่งข้อความด้านการดูแลสุขภาพ: ทีมข้อความใดที่ส่ง
การใช้งานทั่วไป ได้แก่ การแจ้งเตือนการนัดหมาย การยืนยันการจอง บันทึก "เรากำลังดำเนินการล่าช้า" ลิงก์การชำระเงิน การแจ้งเตือนการเรียกคืน และแบบสำรวจความพึงพอใจ การแจ้งเตือนการนัดหมายเป็นเรื่องธรรมดาที่สุด การแจ้งเตือนการนัดหมายอัตโนมัติช่วยประหยัดเวลาการโทรของแผนกต้อนรับ และคำแนะนำของเรา ข้อความเตือนการนัดหมาย shows how to keep them short and clear.
Texting clinical detail, such as results or treatment plans, needs much more care. In most cases, a secure portal or phone call is the better channel.
What to Ask a HIPAA Compliant Texting App or Vendor
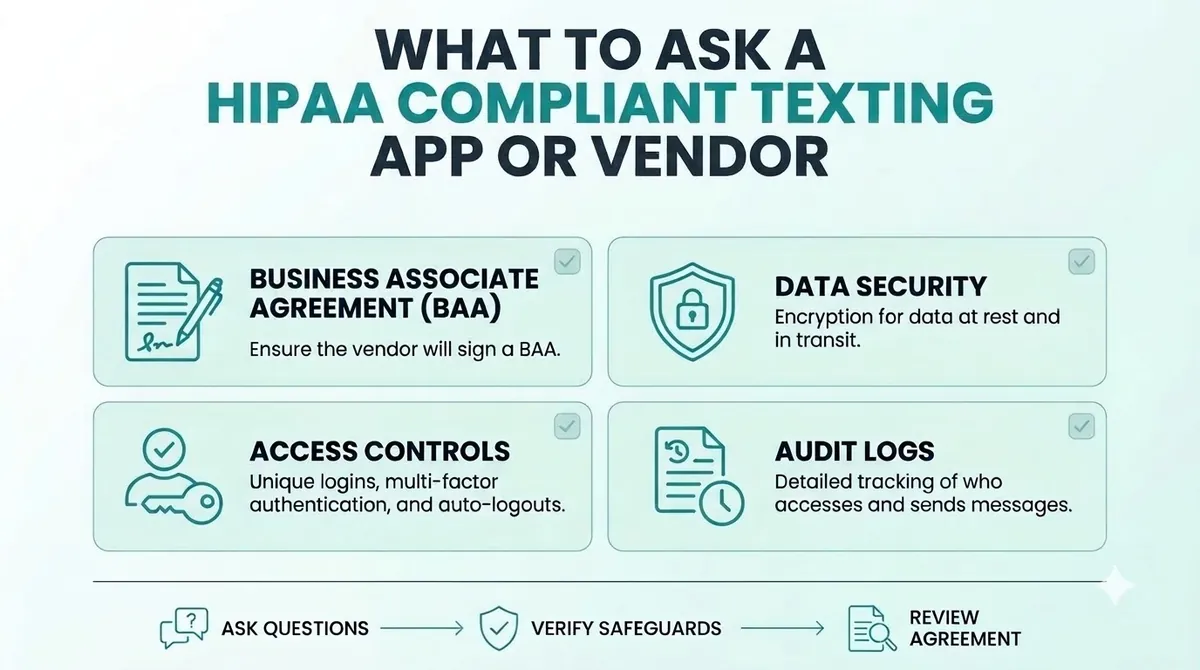
If a texting service will handle PHI for you, the vendor is acting as a business associate. HIPAA says a covered entity may let a business associate create, receive, maintain or transmit PHI only if it obtains satisfactory assurances that the information will be safeguarded. The usual way to do this is a business associate agreement, often called a BAA. For business associate agreement texting, that means getting it signed before any patient messages go out.
Before you choose a HIPAA compliant texting app, appointment reminder software or any other texting service, ask:
- Will you sign a business associate agreement with us?
- How do you protect messages and data while they are sent and stored?
- Who at your company can see our message content?
- How do you handle logins, passcodes and user access?
- Can we remove staff access quickly when someone leaves?
- How long are messages kept, and how are they deleted?
- What happens if there is a security incident?
Get the answers in writing. If a vendor will not sign a BAA, do not send PHI through them. This applies to every vendor, including us. Ask any provider directly before you send patient information.
HIPAA Compliant Texting for Healthcare: A Simple Checklist
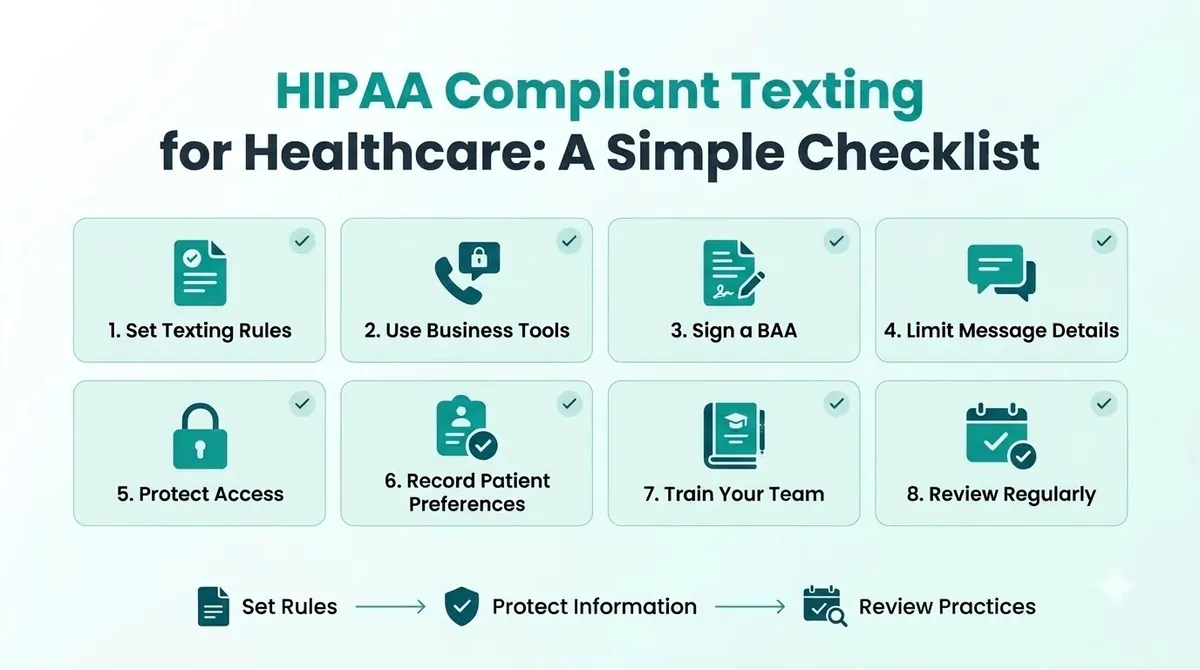
These HIPAA texting best practices are a starting point, not a full compliance program.
1. Decide What You Will and Will Not Text
Write a short list. For example: reminders, confirmations and portal links are fine. Diagnoses, test results and medication names are not.
2. Use Business Tools, Not Personal Phones
Personal phones are hard to control. If an employee leaves or loses their phone, you lose track of patient messages. Use a business tool where you can manage access.
3. Sign a Business Associate Agreement
Do this before you send anything with PHI. Keep a copy.
4. Limit What Each Text Includes
Think "minimum necessary". Use a first name, the clinic name, the time and a way to reply or call. Leave out the reason for the visit.
5. Protect Access
Use unique logins, screen locks and passcodes. Make sure former staff lose access the same day.
6. Get and Record Patient Preferences
Ask patients whether they want texts and which number to use. Record their answer. Our guide to SMS opt in explains how to ask clearly and keep proof.
7. Train Your Team
Everyone who texts patients should know the rules. A one-page guide with safe and unsafe examples is enough to start.
8. Review Regularly
Check your process twice a year, and again when you change tools or add new types of messages.
Common HIPAA Texting Mistakes
- Using personal phones for patient texts. You cannot control or audit them.
- Putting too much detail in the message. Diagnoses and results do not belong in a reminder.
- No agreement with the vendor. If they handle PHI, you need a BAA.
- Texting a wrong or shared number. Confirm numbers and ask patients which number to use.
- Treating HIPAA as the only law. Texts that promote services also fall under TCPA rules.
- Skipping training. One careless text can undo a good process.
HIPAA and the TCPA: Two Different Laws
HIPAA protects health information. SMS marketing compliance is a separate job. The TCPA controls marketing calls and texts, and it asks for consent, honors opt-outs and sets sending hours. A text can follow one and break the other. Some health care messages are treated differently under the TCPA, and our TCPA compliance guide explains how to tell the difference. When you are unsure, get written advice from a lawyer.
HIPAA Compliant Texting Using SMSLocal
SMSLocal is a messaging platform for business texting. We do not claim that using any platform makes you HIPAA compliant. If your messages will include PHI, ask us whether a business associate agreement is available for your account before you send anything, and get the answer in writing. For simple reminders that carry no clinical detail, keeping messages minimal reduces your risk. You can speak to the SMSLocal team about how replies, opt-outs and access work for your account.
Make your messages stand out with reliable, fast and effective communication. Elevate your texting game today.
บทสรุป
HIPAA compliant texting comes down to a few habits. Say less in each message, use business tools, get a business associate agreement when a vendor handles PHI, protect access and train your team.
You do not need to stop texting patients. You need a process you can explain and a vendor who will put their promises in writing.
Start your free trial with SMSLocal and send registered, reliable messages.
คำถามที่พบบ่อย
อาจเป็นไปได้หากคุณใช้การป้องกันที่สมเหตุสมผล HIPAA ไม่ได้ห้ามผู้ป่วยที่ส่งข้อความ แต่ SMS มาตรฐานไม่ได้ออกแบบให้เป็นช่องทางที่เข้ารหัส ลดข้อความให้น้อยที่สุดและใช้เครื่องมือที่คุณควบคุมได้
ข้อความดังกล่าวเป็นไปตามมาตรการป้องกันของ HIPAA สำหรับข้อมูลด้านสุขภาพที่ได้รับการคุ้มครอง นั่นหมายถึงการแบ่งปันขั้นต่ำ การควบคุมการเข้าถึง การปกป้องข้อความระหว่างทาง และการทำข้อตกลงกับผู้จำหน่ายที่จัดการข้อมูล
หากบริการสร้าง รับ ดูแลรักษา หรือส่ง PHI ให้กับคุณ ใช่ HIPAA ต้องการการรับรองที่น่าพอใจจากผู้ร่วมธุรกิจ และข้อตกลงสำหรับผู้ร่วมธุรกิจก็เป็นวิธีปกติในการได้รับการรับประกัน
การปฏิบัติหลายอย่างทำ ใช้ข้อความสั้นๆ ได้แก่ ชื่อ ชื่อคลินิก วันที่และเวลา และวิธีตอบกลับหรือโทรติดต่อ ยกเว้นเหตุผลในการนัดตรวจและรายละเอียดทางคลินิกใดๆ
หลีกเลี่ยงการวินิจฉัย ผลการตรวจ ชื่อยา และรายละเอียดการรักษา ส่งผู้ป่วยไปยังพอร์ทัลที่ปลอดภัยหรือขอให้พวกเขาโทรแทน
แอปบางแอปสร้างขึ้นเพื่อการดูแลสุขภาพ แต่ไม่มีแอปใดที่ทำให้คุณปฏิบัติตามข้อกำหนดได้เพียงลำพัง สอบถามผู้จำหน่ายเกี่ยวกับข้อตกลงร่วมธุรกิจที่ลงนาม และตรวจสอบวิธีจัดการการเข้าถึงและพื้นที่จัดเก็บข้อความ