English
導入
ある歯科医院はノーショーを削減したいと考えており、フロントデスクは個人の電話から患者にテキストメッセージを送信し始めています。 「こんにちは、サム、根管のフォローアップは明日の9時です。」患者の電話がこの手術のことを知らなかった家族と共有されるまでは機能します。
HIPAA 準拠のテキストメッセージ送信が可能です。しかし、それにはルールがあり、上記のクリニックではすでにルールが定められています。
このガイドでは、HIPAA に準拠したテキスト送信について平易な英語で説明します。ルールの内容、どのメッセージがより安全か、テキスト メッセージ ベンダーに何を問い合わせるべきか、簡単なプロセスを設定する方法について説明します。これは一般的な情報であり、法的なアドバイスではありません。 2026 年 11 月に 45 CFR Part 164 のルールテキストを確認しました。
重要なポイント
- HIPAA は患者へのテキストメッセージ送信を禁止していません。保護される健康情報には合理的な保護手段が必要です。
- HIPAA に準拠したテキスト メッセージ送信は、「SMS」という単語だけではなく、テキスト メッセージの送信方法、内容、およびメッセージの処理者によって決まります。
- 最低限のことは共有しましょう。リマインダーに診断名や治療名が必要になることはほとんどありません。
- ベンダーが患者情報を処理する場合は、そのベンダーと業務提携契約を結ぶ必要があります。
- 医療テキスト メッセージは、短くスケジュールされており、臨床的な詳細が含まれていない場合に最適に機能します。
- マーケティングおよびリマインダーのテキストは、TCPA などの他の法律にも適用されます。
- 単独でコンプライアンスに準拠できるツールはありません。ソフトウェアと同じくらいプロセスも重要です。
テキストメッセージは HIPAA に準拠していますか?
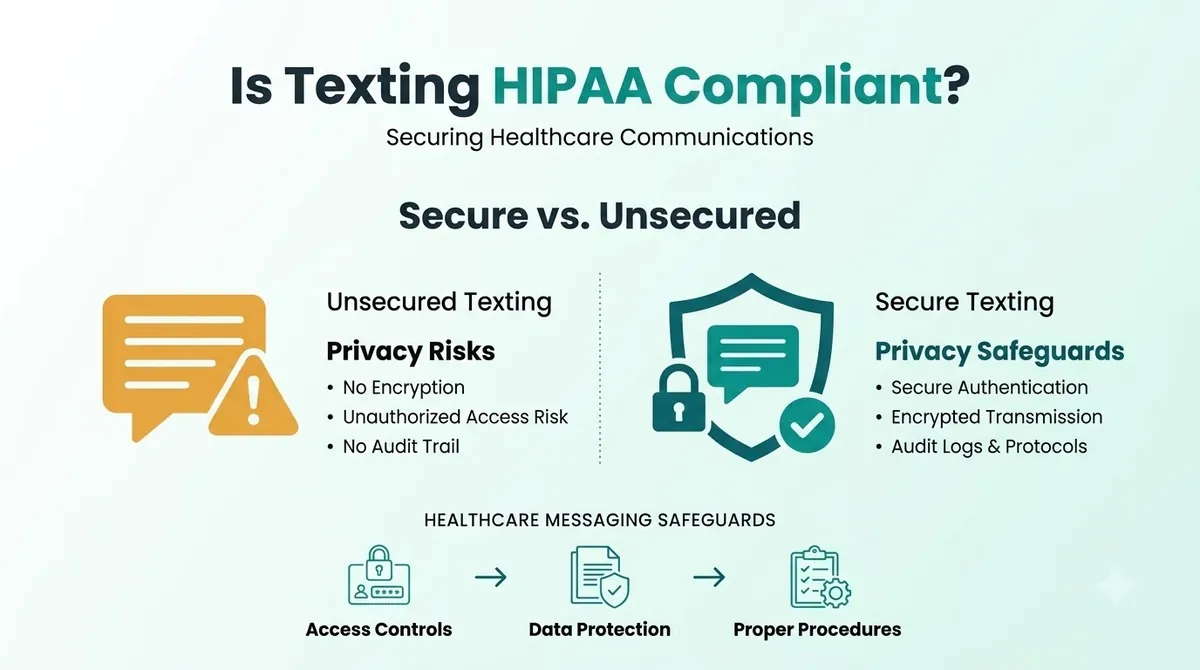
テキスト送信は HIPAA に適合する方法で実行できますが、プレーン テキスト送信は自動的に準拠しません。 HIPAA は、医師、診療所、歯科医、医療保険プランなどの対象となる組織と、それらの組織で働くビジネス関係者のための一連の規則です。メッセージタイプに貼れるスタンプではありません。
標準 SMS は暗号化チャネルとして構築されていないため、HIPAA 準拠の SMS はその使用方法によって異なります。 SMS 暗号化は、プレーン テキストによってデフォルトで提供されるものではありません。メッセージはキャリア ネットワークを経由して携帯電話に留まり、ロック画面に表示されることもあります。そのため、テキストメッセージに何を入力したか、そして誰が電話を閲覧できるかが主なリスクになります。
保護された健康情報 (PHI) は、個人に関連付けることができる健康情報です。名前と予定の種類がよくある例です。 PHI にテキストメッセージを送信するということは、リスクに見合った安全策が必要であることを意味します。
HIPAA テキスト メッセージ ルールの概要
| トピック | それがあなたに求めるもの | それはどこから来たのか |
|---|---|---|
| 送信セキュリティ | ネットワーク経由で送信される PHI への不正アクセスを防ぐための技術的対策 | 45 CFR 164.312(e) |
| 暗号化 | 適切と思われる場合は常に電子 PHI を暗号化します (アドレス可能なアイテム) | 45 CFR 164.312(e)(2)(ii) |
| 必要最低限 | PHI を目的に必要なものに限定する | 45 CFR 164.502(b) |
| 取引先 | PHI を取り扱うベンダーから満足のいく保証を得る | 45 CFR 164.502(e) および 164.308(b) |
| アクセス制御 | 誰が PHI にアクセスしているかを確認し、アクセスを制限する | 45 CFR 164.312(a) および (d) |
「アドレス可能」とはオプションを意味するものではありません。これは、リスクを評価し、対策を適用するか、他のものが同様に優れている理由を文書化することを意味します。
HIPAA 患者へのテキストメッセージ: 通常は問題ないものと危険なもの
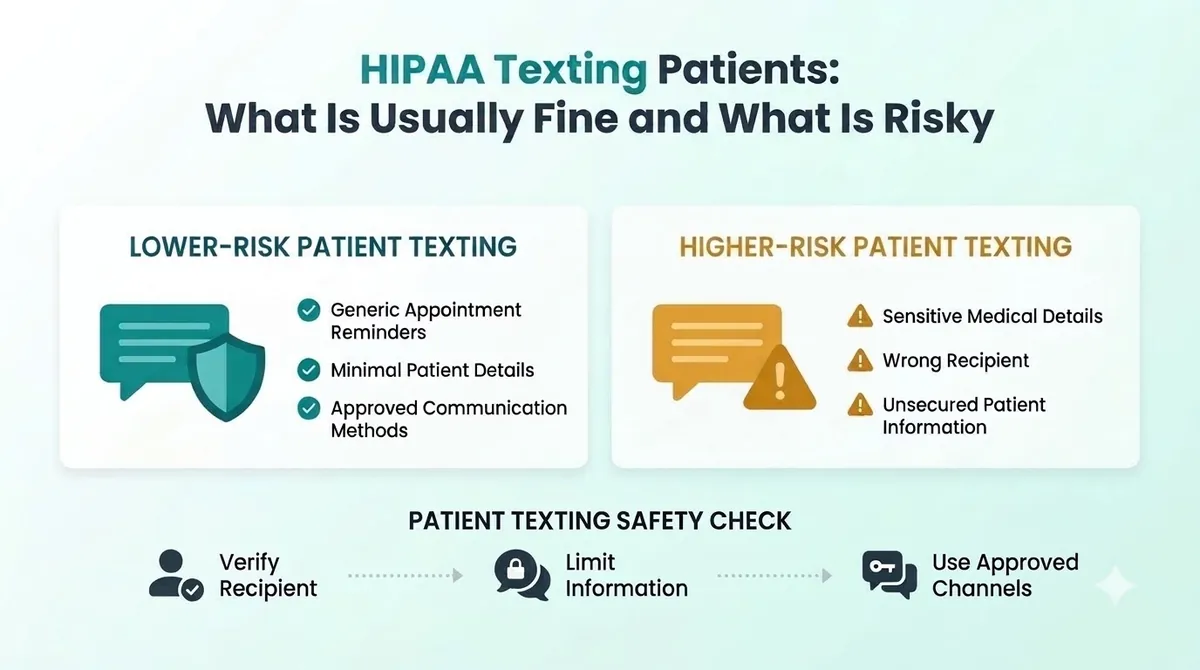
最も安全な文章はほとんど何も語らない。詳細については、患者に安全な場所を案内します。
リスクが低い例 (最小限の情報):
“こんにちは、サム。明日の午前 9 時にブライト スマイル デンタルでの予約のお知らせです。 C と返信して確認するか、カードに記載されている番号にお電話ください。”
“書類の準備ができました。これらを表示するには、患者ポータルにログインしてください。”
リスクの高い例 (情報が多すぎる):
“こんにちは、サム。根管のフォローアップは明日の 9 時です。検査の結果は感染症を示しました。”
“[薬剤名] の処方箋が、[状態] の診断に使用できるようになりました。”
最初のペアは最小値を示します。 2 番目のペアでは、携帯電話を持っている人なら誰でも見ることができるテキストに臨床的な詳細が記載されています。これが、診断、検査結果、投薬を決して含まない HIPAA テキスト メッセージの例を提案する理由です。
ヘルスケア テキスト メッセージング: チームが送信するテキスト
一般的な用途には、予定のリマインダー、予約の確認、「遅れています」のメモ、支払いリンク、リコールのリマインダー、満足度調査などがあります。最も一般的なのは予約のリマインダーです。自動予約リマインダーにより、フロントデスクの電話対応時間を節約できます。 appointment reminder text message shows how to keep them short and clear.
Texting clinical detail, such as results or treatment plans, needs much more care. In most cases, a secure portal or phone call is the better channel.
What to Ask a HIPAA Compliant Texting App or Vendor
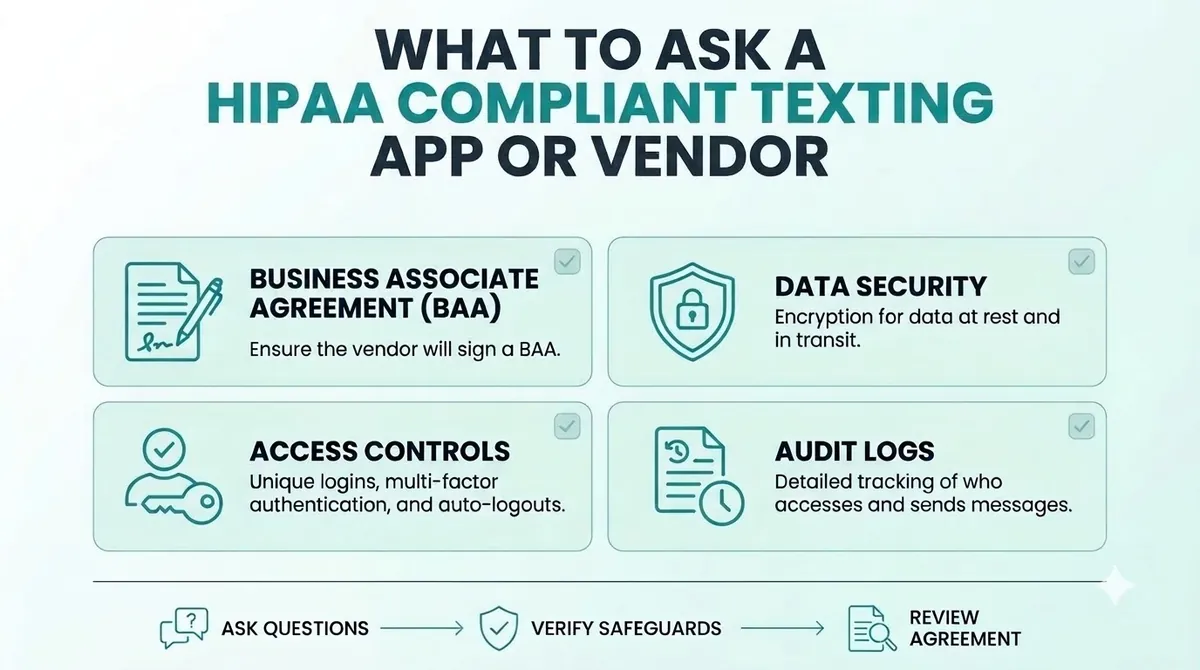
If a texting service will handle PHI for you, the vendor is acting as a business associate. HIPAA says a covered entity may let a business associate create, receive, maintain or transmit PHI only if it obtains satisfactory assurances that the information will be safeguarded. The usual way to do this is a business associate agreement, often called a BAA. For business associate agreement texting, that means getting it signed before any patient messages go out.
Before you choose a HIPAA compliant texting app, appointment reminder software or any other texting service, ask:
- Will you sign a business associate agreement with us?
- How do you protect messages and data while they are sent and stored?
- Who at your company can see our message content?
- How do you handle logins, passcodes and user access?
- Can we remove staff access quickly when someone leaves?
- How long are messages kept, and how are they deleted?
- What happens if there is a security incident?
Get the answers in writing. If a vendor will not sign a BAA, do not send PHI through them. This applies to every vendor, including us. Ask any provider directly before you send patient information.
HIPAA Compliant Texting for Healthcare: A Simple Checklist
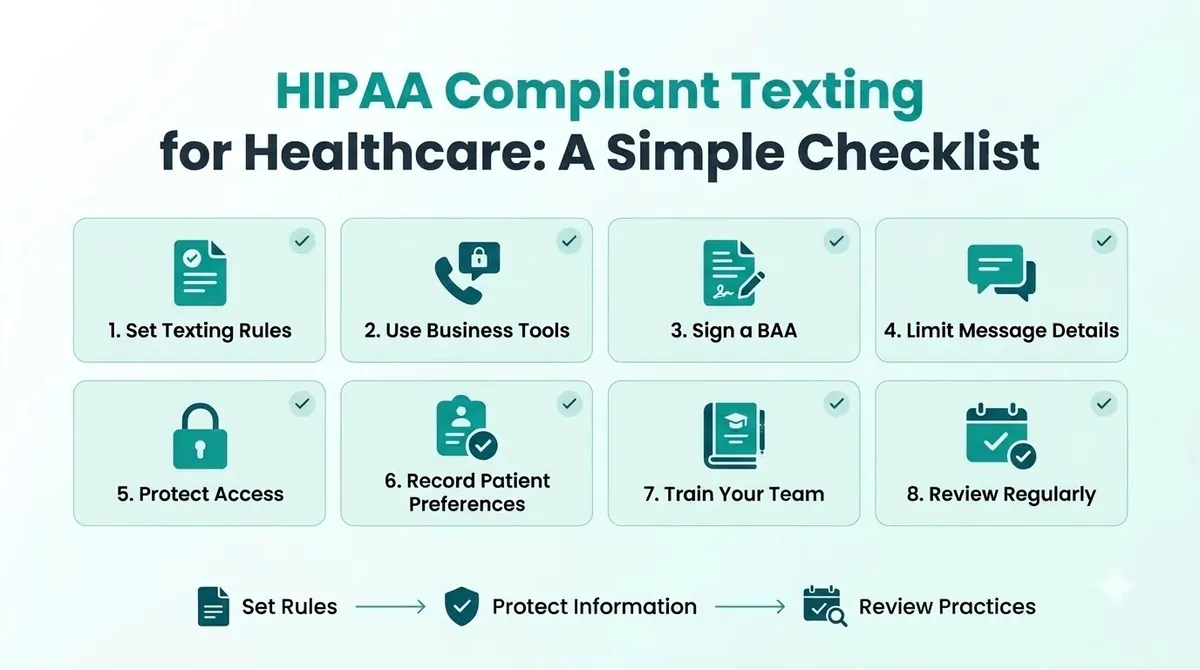
These HIPAA texting best practices are a starting point, not a full compliance program.
1. Decide What You Will and Will Not Text
Write a short list. For example: reminders, confirmations and portal links are fine. Diagnoses, test results and medication names are not.
2. Use Business Tools, Not Personal Phones
Personal phones are hard to control. If an employee leaves or loses their phone, you lose track of patient messages. Use a business tool where you can manage access.
3. Sign a Business Associate Agreement
Do this before you send anything with PHI. Keep a copy.
4. Limit What Each Text Includes
Think "minimum necessary". Use a first name, the clinic name, the time and a way to reply or call. Leave out the reason for the visit.
5. Protect Access
Use unique logins, screen locks and passcodes. Make sure former staff lose access the same day.
6. Get and Record Patient Preferences
Ask patients whether they want texts and which number to use. Record their answer. Our guide to SMS opt in explains how to ask clearly and keep proof.
7. Train Your Team
Everyone who texts patients should know the rules. A one-page guide with safe and unsafe examples is enough to start.
8. Review Regularly
Check your process twice a year, and again when you change tools or add new types of messages.
Common HIPAA Texting Mistakes
- Using personal phones for patient texts. You cannot control or audit them.
- Putting too much detail in the message. Diagnoses and results do not belong in a reminder.
- No agreement with the vendor. If they handle PHI, you need a BAA.
- Texting a wrong or shared number. Confirm numbers and ask patients which number to use.
- Treating HIPAA as the only law. Texts that promote services also fall under TCPA rules.
- Skipping training. One careless text can undo a good process.
HIPAA and the TCPA: Two Different Laws
HIPAA protects health information. SMS marketing compliance is a separate job. The TCPA controls marketing calls and texts, and it asks for consent, honors opt-outs and sets sending hours. A text can follow one and break the other. Some health care messages are treated differently under the TCPA, and our TCPA compliance guide explains how to tell the difference. When you are unsure, get written advice from a lawyer.
HIPAA Compliant Texting Using SMSLocal
SMSLocal is a messaging platform for business texting. We do not claim that using any platform makes you HIPAA compliant. If your messages will include PHI, ask us whether a business associate agreement is available for your account before you send anything, and get the answer in writing. For simple reminders that carry no clinical detail, keeping messages minimal reduces your risk. You can speak to the SMSLocal チーム about how replies, opt-outs and access work for your account.
信頼性が高く、迅速かつ効果的なコミュニケーションにより、メッセージを目立たせることができます。今すぐあなたのテキストメッセージングゲームをレベルアップしましょう。
結論
HIPAA compliant texting comes down to a few habits. Say less in each message, use business tools, get a business associate agreement when a vendor handles PHI, protect access and train your team.
You do not need to stop texting patients. You need a process you can explain and a vendor who will put their promises in writing.
SMSLocal の無料トライアルを開始して、登録された信頼できるメッセージを送信してください。
よくある質問
合理的な安全策を講じれば、それは可能です。 HIPAA は患者へのテキストメッセージ送信を禁止していませんが、標準の SMS は暗号化チャネルになるように設計されていません。メッセージは最小限に抑え、制御できるツールを使用してください。
これは、保護された健康情報に対する HIPAA の保護措置に従ったテキスト メッセージです。つまり、最小限の情報を共有し、アクセスを制御し、転送中のメッセージを保護し、情報を扱うベンダーと契約を結ぶことを意味します。
サービスが PHI を作成、受信、維持、送信する場合は、はい。 HIPAA は取引先からの満足のいく保証を要求しており、取引先契約を取得するのが通常の方法です。
多くの実践がそうしています。本文は短くしてください: 名前、クリニック名、日付と時刻、返信または電話の方法。訪問の理由や臨床上の詳細は省略します。
診断、検査結果、薬の名前、治療の詳細は避けてください。患者を安全なポータルに送るか、代わりに電話するよう依頼してください。
一部のアプリはヘルスケア向けに構築されていますが、それ自体で準拠できるアプリはありません。ベンダーに署名済みの業務提携契約を求め、アクセスとメッセージ ストレージがどのように処理されるかを確認してください。